
POPIA compliance services for your website
We help you prepare your website for POPIA compliance, and for the GDPR if you have visitors in Europe: clear privacy pages, cookie consent, secure forms and collecting only the personal information you need.
Why POPIA compliance matters for your website
The Protection of Personal Information Act 4 of 2013 (POPIA) sets conditions for how organisations in South Africa process personal information. Your website is often where much of that information arrives: contact forms, newsletter sign-ups, online orders, bookings and the analytics tools that track visits.
The Information Regulator is the independent body set up under POPIA to monitor and enforce compliance by public and private bodies, and it deals with complaints from people who feel their personal information has been mishandled.
If you have customers or visitors in the European Union, the EU’s General Data Protection Regulation (GDPR) may apply to you too. The two laws share many of the same ideas, so a website set up carefully for one is usually well on the way for the other.
POPIA compliance is also about trust. People are more willing to fill in a form when they can see how their details will be used and that your site is secure. Clear privacy information and secure forms are good for enquiries as well as compliance.
We look after the website side: the technical setup, the pages and the security. For the legal side, we work with a lawyer who prepares your POPIA compliance documentation and sends it straight to you. That way your website and your paperwork match, and you deal with one team.
Recent work
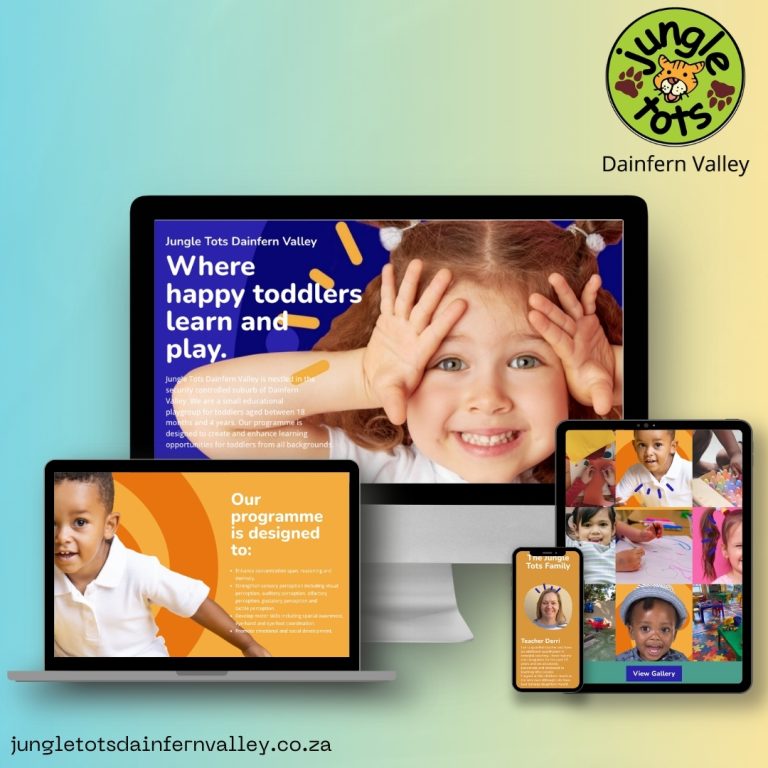
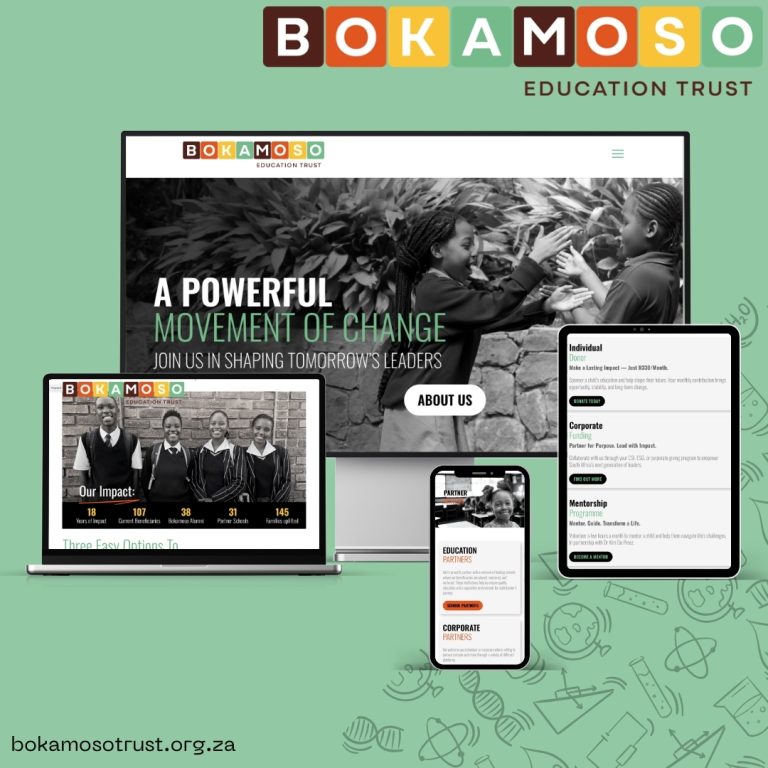
A few of the websites we’ve built for clients, including schools and non-profits that handle personal information every day.
What’s included in our POPIA compliance services
- Privacy policy page: a clear page explaining what you collect and why, linked from your forms and footer, using wording prepared by our lawyer or approved by your own legal adviser
- Cookie consent: a banner that lets visitors accept or decline non-essential cookies, with analytics and marketing tools only loading once they agree
- Consent on forms: opt-in tick boxes for newsletters and marketing that aren’t pre-ticked, with a link to your privacy policy
- Data minimisation: we review every form and remove fields you don’t actually need
- Secure forms: form entries stored securely, spam protection and old entries cleared out on a schedule you choose
- SSL on every page: an encrypted https connection, so information can’t be read in transit
- Access controls: the right user roles, strong passwords, two-factor logins and old accounts removed
- Third-party tools: a check of which plugins and services (analytics, chat, embeds) collect personal information and where it goes
- Security and backups: updates, a firewall, monitoring and offsite backups to keep the data you hold safe
How we work
- Website audit. We look at your forms, cookies, plugins, third-party tools, user accounts and security, and list the POPIA compliance gaps that need attention.
- Fixed quote. You get a clear quote for the changes before any work starts.
- Make the changes. We set up the privacy pages, cookie consent, form changes and security fixes.
- Report back. You get a plain-language summary of what we changed, which you can share with your legal adviser.
- Keep it current. As you add new forms or tools, we check them too, so the site stays in line.
Where personal information enters your website
Most business websites collect personal information in more places than their owners expect. These are the places we review.
| Where it happens | What we check |
|---|---|
| Contact and enquiry forms | Only the fields you need, a link to your privacy policy, secure storage and spam protection |
| Newsletter sign-ups | A clear opt-in that isn’t pre-ticked, and an easy way to unsubscribe |
| Online shops and bookings | SSL at checkout, who can see order details and how long customer records are kept |
| Analytics and tracking | Which cookies and pixels load, and whether they wait for consent |
| Chatbots and embeds | What visitors share and which outside services receive it |
| Website user accounts | User roles, strong passwords, two-factor logins and old accounts removed |
We train you too
We’re happy to keep your website’s POPIA compliance in good shape for you as it changes. What makes us different is that we offer WordPress training to all our clients, so you and your team know how to manage form entries, user accounts and privacy settings yourselves.
Training is one-on-one or for your team, in person or online, and we remain available whenever you need help. See our WordPress courses.
Related services
- Web design: forms and pages planned with privacy in mind from the start
- Website security: firewalls, monitoring and malware removal
- Website maintenance: updates, backups and care plans
- Newsletters: consent-based email marketing
Your questions
Does POPIA apply to my website?
If your website collects personal information about people in South Africa, through contact forms, sign-ups, orders, bookings or tracking tools, then POPIA is relevant to how you handle it. Almost every business website does at least one of these. The lawyer we work with can tell you exactly what your obligations are, and we can show you where your site collects personal information.
Do I need a cookie banner on my website?
A cookie consent banner is the clearest way to tell visitors about tracking tools such as analytics and advertising pixels, and to give them a choice. It is especially important if you have visitors from Europe. We set banners up so tracking only starts after a visitor agrees. Ask your legal adviser what your business specifically needs.
Are you lawyers?
No. We’re a web development team and we handle the technical and website side of compliance. Full POPIA and GDPR compliance also covers your internal processes, policies and contracts, which is legal work. We recommend getting advice from a qualified legal professional, and we’re happy to work alongside them on the website changes they recommend.
What is the difference between POPIA and GDPR?
POPIA is South Africa’s privacy law and the GDPR is the European Union’s. They share many of the same ideas: collect only what you need, be open about how you use it, keep it secure and respect people’s rights over their information. The details differ, so if you have customers in both places, ask your legal adviser which rules apply.
Can you make my existing website POPIA-ready?
Yes, it doesn’t matter who built it. We start with an audit of your forms, cookies, plugins, third-party tools and user accounts, then give you a fixed quote for the changes. Most of the work is practical: privacy and cookie pages, consent tick boxes, removing fields you don’t need, SSL and tightening security.
Do you offer POPIA compliance consulting?
Yes. We offer POPIA compliance through a lawyer we work with, who prepares your POPIA documentation and sends it directly to you, while we handle the website side: privacy and cookie pages, consent, secure forms, data minimisation and access controls. If you already have a legal adviser, we are happy to work with them instead.
Film Industry
Amazing Spaces Locations
Visit site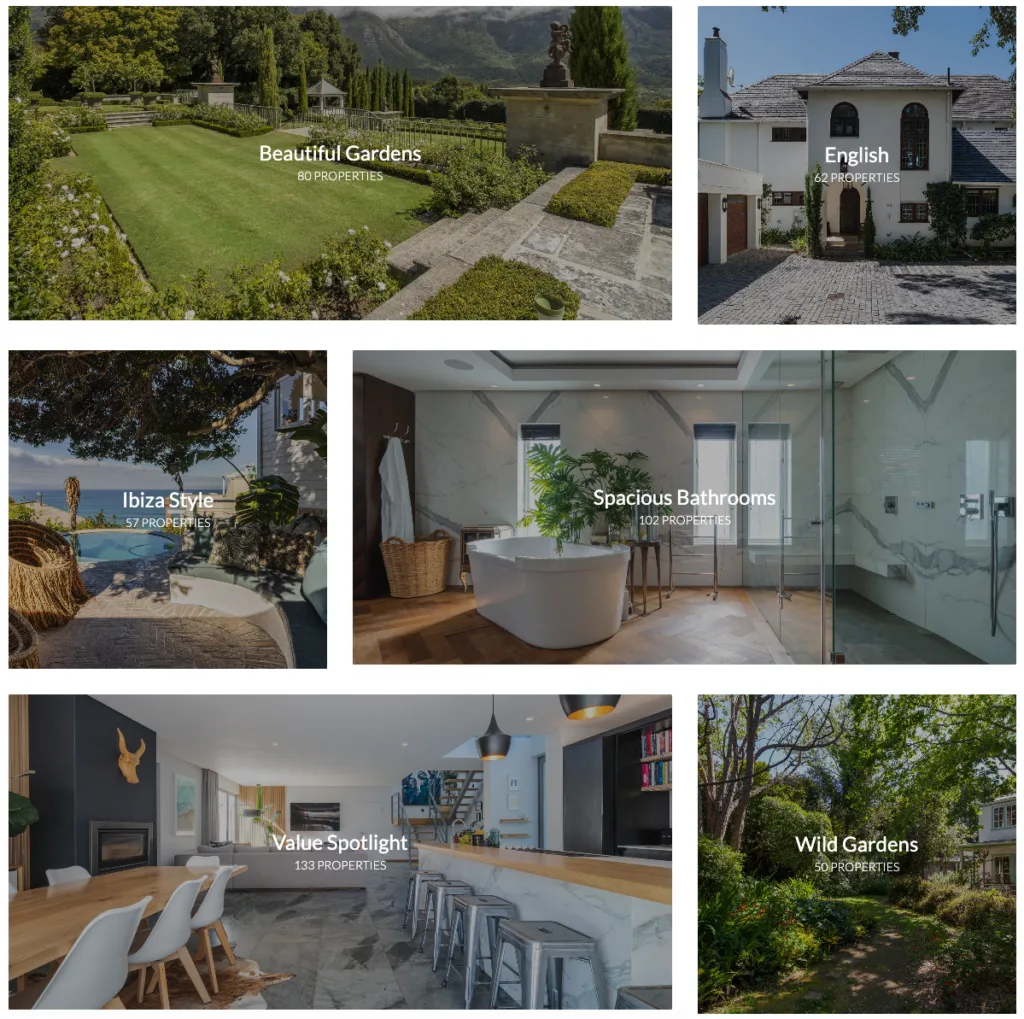
600+
curated locations, many exclusive to the agency
5.0
“I have been working with Clicks Count for many years on various websites. They are always extremely quick to respond, knowledgeable and interprets my needs and the brief perfectly. I cannot recommend them highly enough.”
More ways we can help
Tell us what you need.
You will hear back from Kate or Jeanne within one working day, with a fixed price where we can give one.
- 082 443 6575 Kate
- 083 462 8451 Jeanne
- hello@clickscount.co.za